Topic: infrastructure security
-
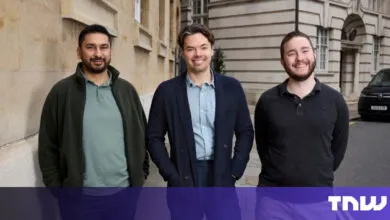
Augur Secures $15M to Safeguard Critical Infrastructure
Augur, a London startup, raised $15 million in seed funding to develop technology that transforms passive surveillance systems into active security tools for critical infrastructure, addressing the gap between data collection and real-time human understanding during crises. The company's mission ...
Read More » -

AgentX Secures Linux Infrastructure Autonomously
Codenotary has launched AgentX, an autonomous platform that uses coordinated networks of AI agents to manage and secure large-scale Linux infrastructure across cloud and on-premises deployments. The platform automates security enforcement, lifecycle management, and operational workflows with a ze...
Read More » -

Bybit Partners with Abu Dhabi to Boost Vietnam's Digital Asset Growth
A major partnership has been announced between Bybit, the Abu Dhabi Blockchain Center, Da Nang City, and Verichains to accelerate Vietnam's digital asset ecosystem and support Da Nang's development into an International Financial Center. The collaboration includes establishing a blockchain regula...
Read More » -

Top Cybersecurity Open-Source Tools: October 2025 Edition
This month's selection of open-source cybersecurity tools offers cost-effective solutions for strengthening security across IT environments, including code analysis and network monitoring. Key tools highlighted include Checkov for infrastructure code scanning, DefectDojo for vulnerability managem...
Read More » -

Xage Fabric: Secure Your Data from Unauthorized Access
Businesses face significant security challenges when adopting AI, including data breaches and unauthorized access, which traditional measures often fail to address effectively. Xage Security has introduced a zero trust platform designed specifically for AI environments, offering identity-centric,...
Read More » -
WWT Launches ARMOR: A Vendor-Agnostic Framework for Secure AI
WWT has launched ARMOR, a vendor-agnostic framework developed with NVIDIA and Texas A&M to secure the entire AI lifecycle from chip design to deployment. The framework is structured around six core security domains, including governance, model security, infrastructure, and data protection, to add...
Read More » -

Qatar Airways Launches IPv6 with CRA to Boost Digital Transformation
Qatar Airways has launched IPv6 across its digital systems, advancing Qatar's digital transformation and aligning with national strategy under the CRA's guidance. IPv6 provides a vastly larger address pool essential for IoT, smart cities, and machine communication, supporting the digital economy'...
Read More » -

Teleport boosts Identity Security platform with AI agent behavior controls
Teleport introduced three new features,Beams Session Summaries, Agentic Classifiers, and Risk Scoring,to keep AI agent behavior within safe boundaries by detecting and preventing agent misalignment in production environments. The company's white paper argues that zero trust is insufficient for go...
Read More » -

Poland's Nuclear Research Center Targeted by Hackers
Poland's National Centre for Nuclear Research successfully thwarted a sophisticated cyberattack, preventing any disruption to its critical operations, including the safe, full-capacity operation of the MARIA research reactor. The centre coordinated with national cybersecurity agencies for a foren...
Read More » -
Bastion: Open-Source Access Control for Complex Infrastructure
The Bastion is an open-source project that centralizes and secures SSH access to infrastructure by acting as a hardened entry point, simplifying credential management and enabling controlled, auditable workflows. It enhances security with strong authentication methods like TOTP and Yubico PIV key...
Read More » -

CISA orders feds to patch critical Joomla bug by Friday
CISA has mandated all U.S. federal agencies patch a maximum-severity vulnerability (CVSS 10.0) in the Joomla Widget Factory JCE plugin by June 19, 2026, due to active exploitation by attackers. The flaw, tracked as CVE-2024-12345, allows unauthenticated remote code execution, potentially leading ...
Read More » -

CISA: Hackers Exploiting Langflow, N-central, Tomcat Flaws
CISA has mandated that federal agencies patch three actively exploited vulnerabilities in IBM Langflow, N-central, and Apache Tomcat within 72 hours, with private sector entities strongly encouraged to remediate as well. The Langflow flaw (CVE-2025-3248) enables unauthenticated remote code execut...
Read More » -
TRA Bahrain, Mobile Operators Launch Anti-SMS Fraud Guidelines
Bahrain's TRA and mobile operators have launched new "Guidelines for Reducing Fraudulent SMS" to combat scam messages and enhance mobile security nationwide. The guidelines establish technical and operational measures for identifying and intercepting fraudulent communications, alongside public ed...
Read More » -

DAEMON Tools Devs Confirm Breach, Release Clean Version
DAEMON Tools Lite was compromised in a supply chain attack affecting free version 12.5.1 installers served from the official website starting April 8, but paid versions of DAEMON Tools products were not impacted. Disc Soft released a clean, updated version 12.6.0 within 12 hours of identifying th...
Read More » -
What CISOs Must Tell the Board About Cyber Risk
CISOs must communicate cybersecurity risks in business terms, focusing on the board's risk oversight duty and how threats could impact the organization's risk appetite. Boards require a synthesized risk index from multiple data sources to understand event probabilities and their financial, operat...
Read More » -
CISA Opens KEV Nomination Form to Vendors and Researchers
CISA has launched a new online nomination form for security researchers and vendors to directly report known exploited vulnerabilities for inclusion in its Known Exploited Vulnerabilities (KEV) catalog, replacing the previous email-only submission process. The agency aims to accelerate the catalo...
Read More » -
Top Cybersecurity Jobs Hiring Now: October 2025
The cybersecurity job market is robust, offering diverse opportunities globally for professionals at all levels to help companies strengthen defenses against evolving threats. Current openings span various roles and locations, including remote, on-site, and hybrid positions, such as Cyber Securit...
Read More » -

Linux kernel LPE flaw, cPanel 0-day exploited for months
A nine-year-old Linux kernel privilege escalation flaw (CVE-2026-31431) and a critical cPanel authentication bypass (CVE-2026-41940) were actively exploited, with proof-of-concept code available for the kernel bug. CISA and Microsoft warned of active zero-day exploitation of a Windows Shell spoof...
Read More » -

Pure Storage Boosts Cyber Resilience with New Innovations & Partnerships
Pure Storage is enhancing cybersecurity by embedding native threat detection into its storage platform and forming strategic partnerships to proactively identify threats and enable faster recovery. The company is integrating with security leaders like CrowdStrike and Superna to provide real-time ...
Read More » -

Microsoft extends zero trust across enterprise AI
Microsoft expanded its Zero Trust Assessment tool with a new AI pillar, adding targeted security checks and enhanced reporting that produce prioritized recommendations and executive summaries for securing AI deployments. The Zero Trust Workshop now includes a DevSecOps pillar with 15 control grou...
Read More »