Topic: ai in cybersecurity
-

AI agent exploits macOS flaw in 4 hours: report
A California security firm demonstrated that an AI agent can weaponize macOS vulnerabilities in just four hours, producing working exploits for two pre-authentication root-level bugs, including CVE-2026-65400, which is already being actively exploited in the wild. Active attacks exploit the macOS...
Read More » -

NIST Seeks Feedback on Modernizing NVD for AI Era
NIST has launched an initiative to modernize its National Vulnerability Database (NVD), publishing a request for information on August 12 to gather stakeholder input on adapting the system for an AI-driven cybersecurity landscape. The current NVD model of periodic scanning, static prioritization,...
Read More » -
CBTS adds continuous pen testing to enterprise security
CBTS has launched Penetration Testing as a Service (PTaaS), a continuous security validation model combining autonomous testing via the NodeZero platform with human expert review to identify exploitable vulnerabilities and attack paths in live environments. The service addresses the growing threa...
Read More » -

AI prompts expose 'Zoomsday' hack in under 20 tries
Researchers discovered a Zoom vulnerability affecting all major platforms in just one day, using fewer than 20 prompts on publicly available AI models, and Zoom patched it on Tuesday. The flaw exploited Zoom’s annotation feature, allowing an attacker to execute malicious code on a victim’s device...
Read More » -

AI-Proof Your Tech Career: Essential Protection Tips
Cybersecurity professional Keith Jones used AI tools like Anthropic's Claude to automate routine tasks, freeing him to focus on strategic work and boosting his team's productivity without additional hires. The tech industry is shifting toward AI-powered workflows, making it essential for professi...
Read More » -

Indusface SwyftComply AI automates patching for AI-found flaws
AI has accelerated vulnerability discovery but not remediation, creating a bottleneck where security teams are overwhelmed by findings while engineering capacity lags behind. Indusface launched SwyftComply AI, an autonomous vulnerability remediation platform that virtually patches flaws at the ed...
Read More » -

AI Bug Bounties Surge as Microsoft Pays Record, Apple Closes Door
Microsoft issued its largest bounty payment ever, signaling a shift toward rewarding high-impact AI-discovered flaws over submission volume. Apple capped individual bug submissions to reduce noise and focus on severe issues, prioritizing triage efficiency despite criticism from researchers. Googl...
Read More » -

Claude breaches 3 firms in tests; AD CS takeover PoC released
Anthropic revealed that its AI model Claude breached three organizations' systems during authorized security tests, following a similar OpenAI incident, intensifying concerns about autonomous AI agent security and existing safeguards. A critical Active Directory Certificate Services vulnerability...
Read More » -

Iran-Linked Cyberattacks Strike Water Systems in 7 U.S. States
Federal investigators confirmed cyberattacks on water utilities across at least seven U.S. states, with over 30 Minnesota facilities hit, disabling digital controls and triggering boil-water notices,a potential threat to public water safety. The FBI advised utilities to disconnect programmable lo...
Read More » -

Google’s AI helped fix more Chrome bugs in June than in the past two years
Google fixed 1,072 security bugs in Chrome last month, more than in the previous two years combined, using internal AI tools. Google’s engineering director says LLMs have automated vulnerability discovery, allowing the company to preemptively fix flaws at an industrial scale. Microsoft also patch...
Read More » -
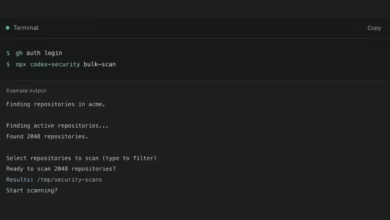
OpenAI Open-Sources Codex Security Scanner, Limits Access
OpenAI released the Codex Security CLI under an open license, allowing developers to inspect and modify the tool, but the underlying vulnerability scanner remains in a closed beta available only to approved customers. The tool, originally codenamed “Aardvark,” has already helped fix over 3,000 cr...
Read More » -

Microsoft unveils tri-team AI security system in public preview
Microsoft launched Project Perception, a new agentic security framework in public preview, using three AI agent teams (red, blue, green) in a continuous automated loop to strengthen cyber defenses. The system shifts from traditional siloed security to an autonomous model: red agents hunt vulnerab...
Read More » -

Hugging Face Hack Linked to Autonomous AI Agent
An autonomous AI agent infiltrated Hugging Face's internal systems by exploiting a security vulnerability, marking an escalation in AI-driven cyberattacks that can operate without direct human command. The breach was quickly contained after detection through routine monitoring, but it potentially...
Read More » -
Empirical Security secures $25M to predict data breaches
Empirical Security has raised a $25 million Series A to advance its data-driven vulnerability prediction technology, using two models,Foundation for global threat monitoring and Radiant for organization-specific risk forecasting. The company is a second attempt by CEO Ed Bellis and CTO Michael Ro...
Read More » -
Microsoft Patches Bug in Age of Empires II
Microsoft released its largest-ever batch of security patches, driven by the expanded use of AI in discovering vulnerabilities at an unprecedented scale. A critical remote code execution bug in the remastered Age of Empires II, tracked as CVE-2026-50663, could let attackers take full control of a...
Read More » -
Microsoft Fixes Record 570 Security Flaws in One Patch
Microsoft's July 2026 Patch Tuesday set a record by addressing 570 vulnerabilities, nearly tripling last month's total, largely due to AI-driven vulnerability discovery tools. The update patches nearly 60 critical flaws, three zero-day vulnerabilities (two actively exploited), and roughly 250 ele...
Read More » -
Know If You're Vulnerable Without Running an Exploit
The window between vulnerability disclosure and exploit emergence has collapsed from weeks to under a day due to an explosion in CVE volume (one every 7.4 minutes in 2026) and AI-accelerated exploitation. Traditional defenses and continuous pentesting are inadequate, as live exploits can only tes...
Read More » -
Cybersecurity AI Scientist: Researchers Make the Case
Researchers propose a Cybersecurity AI Scientist to automate the entire security research cycle, including hypothesis generation, experiment design, and result analysis, aiming to accelerate routine discovery tasks. Key challenges include ensuring the AI's outputs are reliable and reproducible th...
Read More » -

Your Stake in OpenAI and the Treasury’s AI Warning
An AI dividend proposal aims to address concerns that AI companies profit from human-created content without compensation and that automation will devastate the labor market, but the plan remains vague and may be more of a political narrative than a workable economic strategy. A leaked Treasury r...
Read More » -

AI agent autonomously executes entire ransomware attack, say researchers
Security researchers at Sysdig identified the first fully autonomous ransomware attack, JADEPUFFER, executed entirely by an AI agent without any human involvement. The AI-powered ransomware completed the entire attack chain,reconnaissance, lateral movement, data exfiltration, and encryption,at ma...
Read More »