AWS Emulator is a free utility for local service simulation that was developed entirely by autonomous AI agents without human…
Read More »Docker
Entity category: technology
Carbonato is a sophisticated malware strain that compromises unsecured Docker hosts by exploiting exposed daemon APIs to deploy the Hermes…
Read More »
High demand for strategic leadership roles is driving hiring for CISOs, Cyber Security Leads, and IAM Architects across global markets…
Read More »
Uptime Kuma 2.5.0 introduces a 14-day trust delay for npm package updates, reducing supply-chain attack risk during the critical window…
Read More »
Immich is a self-hosted, open-source Google Photos alternative that offers complete ownership of a photo library, overcoming Google's 15GB storage…
Read More »
A Russian state-sponsored hacking group, Laundry Bear, has been exploiting an unpatched Zimbra Collaboration Suite vulnerability (CVE-2025-66376) since July 2025…
Read More »
A massive malware campaign called "FakeGit" uses over 7,600 malicious GitHub repositories to distribute "SmartLoader" and "StealC" malware, achieving over…
Read More »
A GitHub employee's device was compromised after installing a malicious VS Code extension, leading to approximately 3,800 internal repositories being…
Read More »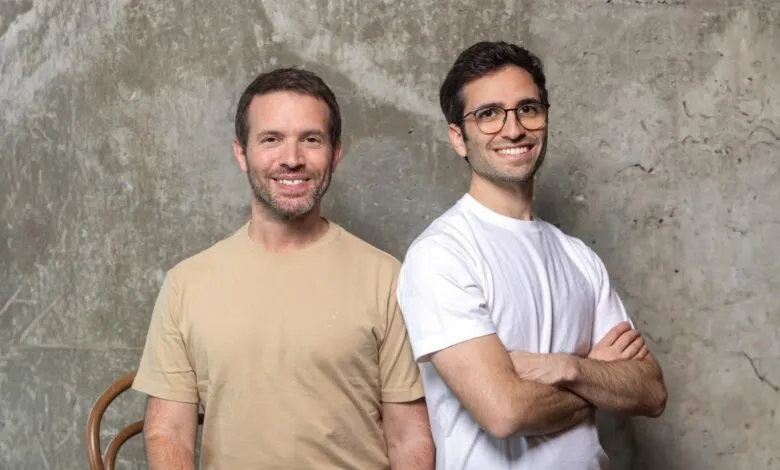
NanoClaw creator Gavriel Cohen and his brother rejected a $20 million acquisition offer and instead closed a $12 million seed…
Read More »
Hacker group TeamPCP published a malicious version (2026.5.09) of the Checkmarx Jenkins AST plugin on the Jenkins Marketplace, marking the…
Read More »
Quasar Linux (QLNX) is a sophisticated new backdoor targeting software developers, combining rootkit, backdoor, and credential-stealing capabilities to infiltrate ecosystems…
Read More »
Attackers are exploiting Amazon Simple Email Service (SES) to bypass email security by routing phishing emails through a trusted platform,…
Read More »
CISA added Linux kernel vulnerability CVE-2026-31431 ("Copy Fail") to its Known Exploited Vulnerabilities catalog due to active exploitation, with a…
Read More »
Attackers exploited a vulnerability in a GitHub action workflow to hijack the open-source package "element-data", downloaded over 1 million times…
Read More »
TeamPCP has not retreated but has strategically paused its supply chain attacks to partner with a new ransomware-as-a-service (RaaS) operation…
Read More »
ShipSec Studio is a new open-source platform that modernizes security operations by providing a dedicated visual, no-code workflow automation layer…
Read More »
A malicious version of the Telnyx SDK Python package was uploaded to PyPI on March 27, 2026, by the threat…
Read More »
The Trivy supply chain attack has escalated with newly discovered malicious Docker images (versions 0.69.5 and 0.69.6) now circulating, broadening…
Read More »
Government entities were the most targeted sector in 2025, enduring 274 distinct cyber attack campaigns, highlighting a critical vulnerability in…
Read More »
Tracebit, a cloud-native deception security startup, has raised $20 million in Series A funding to advance its platform that plants…
Read More »