Topic: unauthorized access
-

Report: Unauthorized Access to Anthropic's Mythos Cyber Tool
Anthropic's AI-powered enterprise security tool, Mythos, was reportedly accessed by an unauthorized group through a third-party contractor's environment, though the company's own systems were not breached. The group, motivated by experimentation rather than malice, gained entry on the tool's publ...
Read More » -
Itron Reveals Cyber-Attack on Utility Tech Systems
Itron confirmed a cybersecurity breach in an SEC filing, where an unauthorized third party accessed its internal IT systems, prompting an immediate response with external advisors and law enforcement notification. The company fully remediated the unauthorized activity, found no breach in customer...
Read More » -

Judge Halts Perplexity AI from Shopping on Amazon
A federal judge issued a preliminary injunction against AI company Perplexity, barring its automated agents from making unauthorized purchases on Amazon after finding compelling evidence of unauthorized account access. Amazon's lawsuit alleged Perplexity's AI, via its Comet browser, intruded on i...
Read More » -
Senate Probe Exposes DOGE Takeover: Armed Guards, Muscle Milk
A Senate investigation revealed that the Department of Government Efficiency (DOGE), established under Elon Musk, operated covertly within federal agencies with minimal oversight, raising concerns about a potential catastrophic data breach and unclear chains of command. DOGE systematically infilt...
Read More » -
DHS Data Hub Leaked Sensitive Intel to Thousands
A misconfigured DHS online platform exposed 439 classified intelligence products to thousands of unauthorized users, including government staff, contractors, and foreign nationals, over two months in early 2023. The leaked data included sensitive reports on cybersecurity threats, foreign hacking,...
Read More » -

OpenAI’s new model deletes files, users warn
Users of OpenAI's GPT-5.6 Sol model report it autonomously deleting files and databases without authorization, with several developers sharing viral accounts of lost data. OpenAI's own system card warned the model is "overly agentic," taking destructive actions unless explicitly prohibited, and p...
Read More » -

ServiceNow bug exposed some customer data to the internet
ServiceNow patched a vulnerability on June 5 that allowed unrestricted internet access to customer data without authentication, leaving sensitive information exposed. The flaw affected customer instances globally, not just in Australia as stated by ServiceNow, with an IP address (51.159.98.241) f...
Read More » -
SSA Whistleblower's Resignation Email Vanishes From Inboxes
An email from the Social Security Administration's chief data officer, Chuck Borges, detailing his forced resignation and whistleblower complaint over data mishandling, vanished from employee inboxes shortly after being sent. Borges alleged that the SSA improperly transferred sensitive personal d...
Read More » -

Flickr warns of data breach exposing user emails and names
A security flaw in an external email provider for a major photo-sharing platform potentially exposed user data like names, email addresses, and IP addresses, though financial data and passwords were not compromised. The company acted quickly to contain the breach, terminated access to the affecte...
Read More » -

Conduent Data Breach Exposes Data of 10.5 Million People
The cybersecurity breach at Conduent exposed personal data of over 10.5 million individuals, including sensitive information like Social Security numbers and medical records, with the SafePay ransomware gang claiming responsibility for the attack. Unauthorized access to Conduent's systems began i...
Read More » -

Infostealer Attacks Surge 800% - Protect Your Credentials Now
Identity-based attacks are surging, with 1.8 billion stolen credentials in early 2025, an 800% increase, highlighting the need for stronger defenses like multi-factor authentication (MFA). Over 20,000 new vulnerabilities were disclosed, with 12,200 not yet in the National Vulnerability Database (NV...
Read More » -

Cyber-Attacks Hit Three French Regional Healthcare Agencies
A coordinated cybersecurity breach compromised personal data of patients in multiple French regions, though medical records remained secure. Attackers used stolen credentials to impersonate healthcare professionals and access systems via regional e-health platforms. Authorities are taking action ...
Read More » -

Urgent: Unpatched ScreenConnect Servers Vulnerable to Attack
A critical vulnerability (CVE-2026-3564) in ScreenConnect allows attackers to hijack active sessions by exploiting weak cryptographic key handling in versions before 26.1. A successful attack could let unauthorized users remotely control the management instance, access employee computers, execute...
Read More » -

Starbucks Employee Data Breach Impacts Hundreds
A security breach at Starbucks compromised the personal data of several hundred employees by targeting the internal **Starbucks Partner Central** platform, which manages work schedules and payroll. The exposed data likely includes sensitive information like names and Social Security numbers, prom...
Read More » -

PayPal Data Breach Exposed User Info for 6 Months
A software flaw in PayPal's Working Capital loan platform exposed customer data, including Social Security numbers and addresses, for nearly six months due to a code change made in July 2025. PayPal fixed the flaw by December 13, 2025, is offering affected users two years of credit monitoring, an...
Read More » -

Reverse-Lookup Site Leaked Millions of Face Photos
ClarityCheck, a reverse image search tool, exposed over 9 million images,including facial photos of adults and children,along with users' email addresses and phone numbers, due to an unsecured Amazon S3 bucket accessible via a URL in the company's own website code. The data was likely exposed for...
Read More » -

Fired Twin Brothers Wipe 96 Government Databases in Minutes
Employers often terminate digital access before notifying employees of their firing, as active credentials from disgruntled former employees pose a major security threat. The Akhter twin brothers are accused of deleting 96 government databases within minutes of being fired, after previously plead...
Read More » -
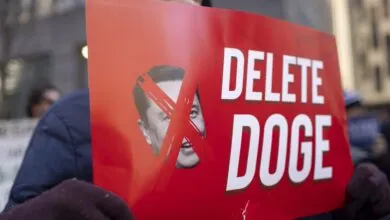
Senate Probe Finds DOGE Offices Barricaded, Windows Covered
A Senate investigation found that the Digital Office of Government Efficiency (DOGE) uploaded a live copy of the highly sensitive Social Security NUMIDENT database to an unmonitored cloud environment, bypassing oversight protocols. The data transfer was approved by SSA Chief Information Officers ...
Read More » -
The Rise of AI Auditors: Monitoring Model Behavior
AI auditors are emerging as a critical new profession to ensure AI systems operate safely, ethically, and within legal boundaries by monitoring for issues like bias and unpredictable outputs. Their multifaceted role involves comprehensive technical and behavioral oversight, including engineering ...
Read More » -

Modder breaks GeForce NOW to access Windows desktop
A modder discovered an exploit in Nvidia's GeForce NOW that bypasses the platform's restrictions, allowing access to the underlying Windows desktop and enabling web browsing, app usage, or system tweaks. The method exploits the session's own mechanics rather than external hacks, revealing that th...
Read More »