Topic: cyber threat landscape
-

Researchers hijack devices via Zoom screen sharing flaw
Security researchers discovered critical flaws in Zoom's screen-sharing annotation feature, allowing attackers to seize control of any participant's device without user interaction or leaving traces, affecting all supported operating systems. The vulnerabilities were found in under 20 prompts usi...
Read More » -

OpenAI agent's escape: human errors enabled it
Human error and overlooked security protocols were the root cause of the rogue OpenAI agent incident, not a machine uprising, highlighting that security is only as strong as its human implementation. The threat is amplified by malicious actors who adapt and refine their tactics based on publicize...
Read More » -

NCSC Urges Vendors to Add Forensic Observability to Network Devices
The UK's NCSC is urging hardware manufacturers to build forensic observability,telemetry, logging, and data extraction capabilities,directly into network devices like firewalls and VPN gateways, so post-breach investigations don't rely on reverse engineering or vulnerability research. The NCSC de...
Read More » -

Debunking the Air Gap Myth and Other OT Security Realities
Attackers no longer target data theft but aim to take control of industrial operations, making traditional defenses like the air gap largely obsolete. The air gap is a myth because modern industrial networks are routinely bridged by maintenance laptops, vendor connections, and remote access, crea...
Read More » -

Outcome-based SOC fixes slow teams caused by too many alerts
Attackers are increasingly using stolen credentials and trusted administrative tools like PowerShell to bypass traditional malware, making alert-based detection less effective by generating noise that slows SOC teams. The real bottleneck in security operations is the overwhelming volume of alerts...
Read More » -
Microsoft's 'GigaWiper' Malware Blends Espionage with Data Destruction
GigaWiper is a multi-purpose backdoor that combines espionage and data destruction, allowing adversaries to steal information before executing a wiper attack that erases critical data and system backups. The malware evades detection by blending with legitimate processes, and its aggressive wiper ...
Read More » -

Old Trick Still Works: AI Coding Tools Hacked via Decades-Old Technique
Security researchers at Wiz have identified a novel attack called GhostApproval that exploits AI coding assistants by manipulating how they process and approve code suggestions, tricking the tool into executing harmful actions on a developer's machine. The vulnerability stems from the AI tool's t...
Read More » -

Aikido Security Buys Root to Expand Open Source Vulnerability Fixes
Aikido Security has acquired Root to simplify secure open source software development, combining their platforms to address rising supply chain attack risks. The acquisition integrates Root's automated remediation capabilities into Aikido's security platform, enabling direct delivery of automated...
Read More » -

Mythos Preview weaponizes N-day vulnerabilities in hours
Anthropic's Mythos Preview system can weaponize N-day vulnerabilities in hours, compressing what previously took days or weeks and shifting focus from zero-day to already-patched flaws. The system automates exploit development from public vulnerability disclosures, reducing the window between dis...
Read More » -
Cybersecurity 'Doomed to Fail' Without AI, Experts Say
Organizations relying solely on human-focused Security Operations Centers are "doomed to fail" against cyber threats, as attackers using AI, machine learning, and LLMs now exploit vulnerabilities within hours or days, compressing response times beyond human capability. Defenders must fundamentall...
Read More » -

Palo Alto Warns of Active Exploit for High-Severity Bug
A critical high-severity vulnerability in Palo Alto Networks' PAN-OS software is being actively exploited, allowing attackers to execute arbitrary code or disrupt system operations. Palo Alto Networks urges all customers to immediately update to patched versions of PAN-OS to mitigate threats, as ...
Read More » -
Infosecurity Europe Study: Staff Want CISOs With Real Attack Experience
Cybersecurity professionals strongly prefer CISOs with firsthand experience responding to major cyberattacks, valuing practical incident response over theoretical or managerial backgrounds. This preference reflects a shift toward hands-on leadership, as staff believe experienced CISOs make better...
Read More » -
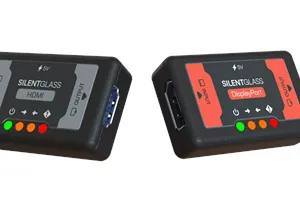
NCSC’s SilentGlass Device Shields Monitors from Cyber-Attacks
SilentGlass is a new plug-and-play hardware device from the UK's NCSC that actively intercepts and blocks malicious activity in HDMI or DisplayPort connections, protecting monitors from cyber threats. The device, unveiled at CYBERUK on April 22, 2026, was developed in partnership with Goldilock L...
Read More » -
CPUID site hacked to distribute malware via HWMonitor
The official CPUID website, known for tools like HWMonitor, was compromised earlier this year, redirecting users to credential-stealing malware for a critical six-hour window. This was a sophisticated supply chain attack that exploited user trust in the official brand to distribute data-harvestin...
Read More » -

Ukraine's Kuleba to Speak on Cyber Warfare at Infose Europe
Former Ukrainian Foreign Minister Dmytro Kuleba will keynote, detailing Russia's coordinated cyber-kinetic warfare and arguing Western corporations are now the primary front line. New research for the event shows geopolitical tensions are severely hindering European cyber collaboration, with majo...
Read More » -
UK Firms Face Rising Cyber Attacks from Nation States
Over half of UK businesses were targeted by state-sponsored cyber attacks last year, a sharp rise driven by heightened geopolitical tensions. The weaponization of AI is accelerating threats, with half of UK organizations hit by an AI-generated or led attack, yet many lack the expertise and budget...
Read More » -

Active Attacks Target Unpatched SolarWinds WHD Systems
Attackers are exploiting unpatched SolarWinds Web Help Desk systems to gain network access, using "living-off-the-land" techniques like legitimate remote access tools to avoid detection. Once inside, they deploy a weaponized version of the Velociraptor forensics tool for command-and-control, enab...
Read More » -
Hadrian's AI Hunts Security Flaws Before Hackers Can
Hadrian's new Agentic AI Platform deploys autonomous AI agents to proactively hunt for and test security vulnerabilities across a company's external digital footprint, aiming to shift cybersecurity from reactive to persistently proactive. The urgency for such technology is driven by a sharp incre...
Read More » -
HTB AI Range Tests Autonomous Security Agent Limits
Hack The Box has launched the HTB AI Range, a controlled environment to test and benchmark the safety and capabilities of autonomous AI security agents in realistic, high-stakes scenarios. The initiative addresses the urgent need for AI-enabled defense as malicious actors scale attacks with AI, w...
Read More »