Topic: attack attribution
-

Hijacked Hotel Wi-Fi Spreads Spyware Via Fake Updates
CaptiveCrunch is a malicious campaign exploiting compromised hotel Wi-Fi captive portals to redirect travelers to fake browser update pages, delivering the CornFlake remote access trojan that can spy via webcam, microphone, keyboard, and steal credentials. The attack leverages DNS manipulation on...
Read More » -

Poland Thwarts Cyberattack on Energy Grid
Polish authorities successfully prevented a sophisticated cyberattack on the country's energy infrastructure in late December, which used a new data-wiping malware called DynoWiper. The attack is attributed with medium confidence to the Russia-aligned Sandworm APT, a group linked to Russian milit...
Read More » -

Cisco FMC Flaw Exploited Before Patch (CVE-2026-20131)
The Interlock ransomware gang exploited a critical zero-day vulnerability (CVE-2026-20131) in Cisco's Secure Firewall Management Center for over a month before a patch was released, using it for arbitrary code execution and privilege escalation. Amazon's threat intelligence, using a honeypot, unc...
Read More » -

SmarterTools Breached by Hackers Exploiting Own Software Flaw
The Warlock ransomware gang breached SmarterTools by exploiting an unpatched SmarterMail server, demonstrating how a single overlooked system can compromise an entire network. Attackers used a specific authentication bypass vulnerability to gain access, moved laterally with Windows tools, but wer...
Read More » -

Ransomware Attack Hits SmarterMail via Critical Flaw
A ransomware attack on SmarterTools began via an unpatched, employee-created virtual machine running outdated SmarterMail software, which allowed lateral movement into office and data center networks. The breach, attributed to the Warlock group exploiting a known vulnerability, led the company to...
Read More » -

Why Sanctions Can't Stop Cyberattacks - But Still Hurt
Sanctions impose operational friction on state-sponsored cyber attackers by increasing costs and forcing them to adapt, though they rarely stop malicious activities entirely. The most effective sanctions target the broader ecosystem enabling cyber operations, such as cryptocurrency mixers and tec...
Read More » -

How ShinyHunters Hackers Exploit SSO to Steal Cloud Data
The ShinyHunters group uses sophisticated voice phishing (vishing) to steal employee credentials and bypass multi-factor authentication by impersonating IT support and using fake login pages. Once inside via a compromised single sign-on (SSO) account, attackers gain a centralized springboard to a...
Read More » -

Microsoft Teams Targeted by Fake IT Support Scams
A new wave of phishing attacks is exploiting Microsoft Teams, using fake IT support accounts to trick employees into installing malware that gives attackers full network control. Attackers are shifting from email to Teams due to its trusted role in business, impersonating IT staff to deploy remot...
Read More » -
Massive supply-chain breach exposes terabytes of credentials
A supply-chain attack on LiteLLM, an open-source AI platform, exposed credentials from major organizations like Microsoft, Amazon, and Cisco, with data pulled from the official Python Package Index during a 40-minute window in March. The stolen data includes cloud keys, SSH keys, Kubernetes secre...
Read More » -

Drift Protocol Pauses Transfers After $2M Exploit
Drift Protocol has suspended all transfers to contain a major security breach, with initial loss estimates varying widely. Conflicting reports from security firms suggest losses could be between $136 million and $285 million, potentially making it the largest crypto theft of 2026. The attack's pe...
Read More » -
Hackers Target Unpatched Fortinet Flaws After Fix
Attackers are exploiting two critical authentication bypass vulnerabilities (CVE-2025-59718 & CVE-2025-59719) in Fortinet products, gaining administrative access to steal sensitive system configuration files. The theft of these configuration files poses a severe risk, exposing network details and...
Read More » -

Cyberattack Grounds Check-Ins at Major European Airports
A cyberattack on Collins Aerospace's MUSE software disrupted automated check-in and baggage systems at major European airports, forcing a switch to slower manual processes. The incident highlighted a critical vulnerability in the aviation sector's digital supply chain, as the attack targeted a th...
Read More » -

Poland's Nuclear Research Center Targeted by Hackers
Poland's National Centre for Nuclear Research successfully thwarted a sophisticated cyberattack, preventing any disruption to its critical operations, including the safe, full-capacity operation of the MARIA research reactor. The centre coordinated with national cybersecurity agencies for a foren...
Read More » -
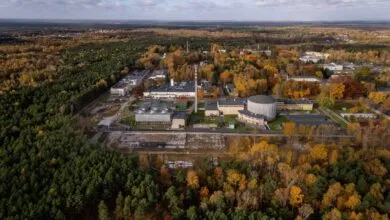
Cyberattack Strikes Poland's Nuclear Research Center
Poland's National Centre for Nuclear Research (NCBJ) successfully neutralized a sophisticated cyber attack using its early detection systems and security protocols, preventing any compromise to its operations. The incident had no impact on the safety or operation of the MARIA research reactor, wh...
Read More » -

eScan AV Users Hit by Malicious Update Attack
Unknown attackers compromised eScan's update server, weaponizing it to deploy a malicious downloader that disabled the antivirus and blocked future security updates. The breach, detected in January 2026, forced the vendor to take its global update system offline and required many users to manuall...
Read More » -

Baker University Data Breach Exposes 53,000 People in 2025
A data breach at Baker University compromised the sensitive personal information of over 53,000 individuals, including Social Security numbers, financial details, and medical records. The university discovered unauthorized network access in December 2024 and is offering credit monitoring, but has...
Read More » -

Urgent Samsung Patch Stops Spyware Exploit
Samsung has released a critical security update for a vulnerability (CVE-2025-21042) in its image processing library, which was actively exploited to install the LANDFALL spyware on mobile devices. The spyware uses a zero-click infection method via manipulated image files, allowing it to infect d...
Read More » -

Stealth Malware Campaign Infects Thousands via DNS TXT Abuse
The Detour Dog malware campaign has infected over 30,000 websites, using DNS TXT records for server-side attacks that remain hidden from most users, selectively targeting specific visitors for redirection or malware downloads. This attack operates by having compromised servers send DNS queries wi...
Read More » -

Crimson Collective Hackers Breach AWS for Data Theft
The Crimson Collective is a hacking group infiltrating AWS infrastructures to steal sensitive data and extort organizations, as seen in a breach at Red GitLab repositories. Attackers compromise AWS using exposed credentials and tools like TruffleHog, then escalate privileges to gain administrativ...
Read More » -
Ukraine's Military Targeted in Deceptive Charity Malware Attack
A Russian-aligned threat group (Void Blizzard/Laundry Bear) targeted Ukrainian military personnel in late 2025/early 2026 using a fake charity scheme to deploy the PluggyApe backdoor malware. The attack used personalized messages on encrypted apps to trick victims into downloading malicious files...
Read More »