2 Suspects Arrested in TeamPCP Hacking Group Probe
▼ Summary
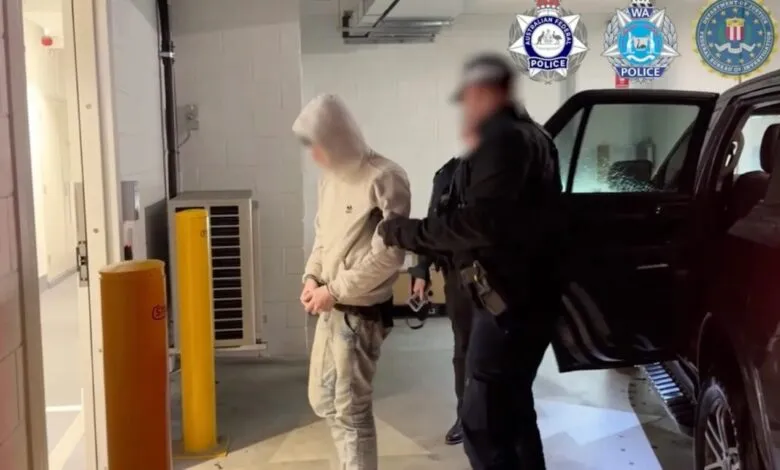
– Authorities in Australia arrested two men accused of participating in cybercrimes for the hacker group TeamPCP.
– The duo faces 14 charges related to their involvement in a prolific campaign that infected over 1,000 organizations globally.
– TeamPCP is known for executing supply chain attacks by infecting open source software packages with malware.
– The worm, named Shai-Hulud, propagated through CI/CD pipelines to compromise developers’ future software updates.
– The investigation revealed the suspects lived in Western Australian towns and were identified through detailed reporting on their mistakes.
Australian authorities have apprehended two individuals linked to TeamPCP, a notorious hacker collective responsible for a massive global supply chain campaign. The group executed a relentless series of attacks over a nine-month period, ultimately compromising the systems of more than 1,000 organizations worldwide.
The Australian Federal Police confirmed the arrests on Wednesday, stating that the suspects were charged with 14 separate offenses. While official statements did not release their names, they identified the men as residents of the Western Australian towns of Cottesloe and Mandurah. The investigation into TeamPCP has been extensive, with KrebsOnSecurity providing detailed backgrounds on the defendants and outlining the specific errors that led to their capture.
A Relentless Supply Chain Campaign
Since emerging in December, TeamPCP has become a persistent headache for security professionals and law enforcement agencies globally. The group distinguished itself through a sophisticated strategy of infecting open-source software repositories. By lacing these packages with malware, the hackers created a self-propagating threat that spread from one package to another across the digital ecosystem.
The core of this operation targeted CI/CD pipelines, the automated processes used by developers to build, test, and deploy code. This approach allowed the attackers to infiltrate numerous organizations simultaneously by compromising the tools developers relied upon daily.
The Shai-Hulud Worm
Once an organization’s pipeline was breached, a specific piece of malware known as Shai-Hulud took hold. This worm was designed to attach itself to future updates of the compromised packages. As developers downloaded these tainted tools and processed them through their own CI/CD platforms, their internal software environments became infected. This method ensured that the breach propagated rapidly, turning individual compromises into widespread incidents across multiple networks.
(Source: Ars Technica)