Topic: defensive recommendations
-

CISA Mandates US Agencies Patch Critical Cisco Vulnerability
CISA has mandated federal agencies to patch a critical Cisco firewall management vulnerability (CVE-2026-20131) within three days, as ransomware groups are actively exploiting it. The flaw, with a maximum severity score, allows unauthenticated attackers to execute arbitrary code with root privile...
Read More » -
Scattered Spider Now Targets VMware vSphere in New Attacks
A cybercrime group, Scattered Spider (UNC3944), is targeting VMware vSphere environments in critical industries like retail, airlines, and insurance using social engineering and hypervisor-level exploitation. The attackers use phone-based impersonation to gain credentials, escalate access to vCen...
Read More » -
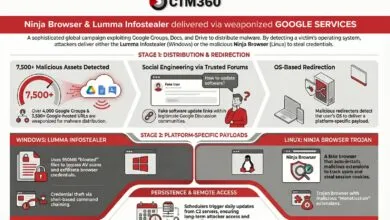
Lumma Stealer & Ninja Malware Hijack Google Groups
A widespread malware campaign exploits Google's trusted services, using over 4,000 malicious Google Groups and 3,500 Google-hosted URLs to distribute information-stealers by disguising links as legitimate resources. The attack deploys the Lumma Stealer on Windows via deceptive archives and target...
Read More » -

TeamPCP Ransomware Shift Raises Threat Despite Slower Attacks
TeamPCP has not retreated but has strategically paused its supply chain attacks to partner with a new ransomware-as-a-service (RaaS) operation called Vect, aiming to monetize stolen credentials. The group has rapidly evolved since 2024, building automated attack capabilities and demonstrating ada...
Read More »